Secure AI Starts with Control
Why businesses should build purpose-specific AI systems around their own rules, protected information and accountable decisions.
A convincing answer can still be wrong. A useful document can still contain confidential information. An automated action can still exceed the authority of the person who requested it.
These are practical concerns for any company introducing artificial intelligence into its operations. The business question is therefore broader than which model produces the most impressive response. Companies must decide what their AI may access, which tasks it may perform and how its results will be checked.
For sensitive business functions, there is a strong case for dedicated AI systems: engines configured for defined purposes, governed by company-controlled workflows and connected only to the information and tools they need.
Fluent language is not verified knowledge
General-purpose generative AI can produce clear explanations, useful drafts and plausible analyses. Its fluency can also conceal unsupported conclusions.
The US National Institute of Standards and Technology identifies "confabulation" as a significant generative AI risk: systems may confidently produce false information, inconsistent reasoning or fabricated supporting references. These failures become particularly consequential when people rely on the output to make important decisions.
In a business setting, a model might misinterpret a contractual obligation, overlook a qualification in a technical report or present an outdated requirement as current. These are illustrative scenarios, but they explain why a polished answer should never be treated as sufficient evidence.
A dedicated system can require document references, restrict the sources used and flag missing information. Those controls reduce opportunities for unsupported answers; they do not eliminate the need to test the system and verify its conclusions.
Confidentiality requires a clear data boundary
Businesses hold information that should not move freely between employees, departments, suppliers or external services: customer records, legal correspondence, product designs, financial forecasts and internal investigations.
Before introducing AI, management needs clear answers. Where are prompts and documents processed? Who can access them? How long are they retained? Can they be used for model training? What happens to logs, backups and information retrieved from connected systems?
The answers depend on the provider, contract, configuration and deployment. External AI services should not all be treated as equivalent, and uploading information does not universally mean that it will be used for training.
Personal data creates additional responsibilities. The European Data Protection Board has explained that AI models trained with personal data cannot automatically be considered anonymous; that assessment depends on the circumstances and the likelihood of identifying individuals or extracting their information.
A privately operated environment can give a company greater control over these boundaries. However, local hosting alone does not establish lawful processing, sound access controls or secure operation.
Own the rules that govern the work
Building a company-controlled AI engine does not necessarily mean training a foundation model from scratch.
A business can use an existing model while developing its own application, retrieval methods, validation rules, permissions and approval processes. What matters is whether the organisation controls how the model participates in its work.
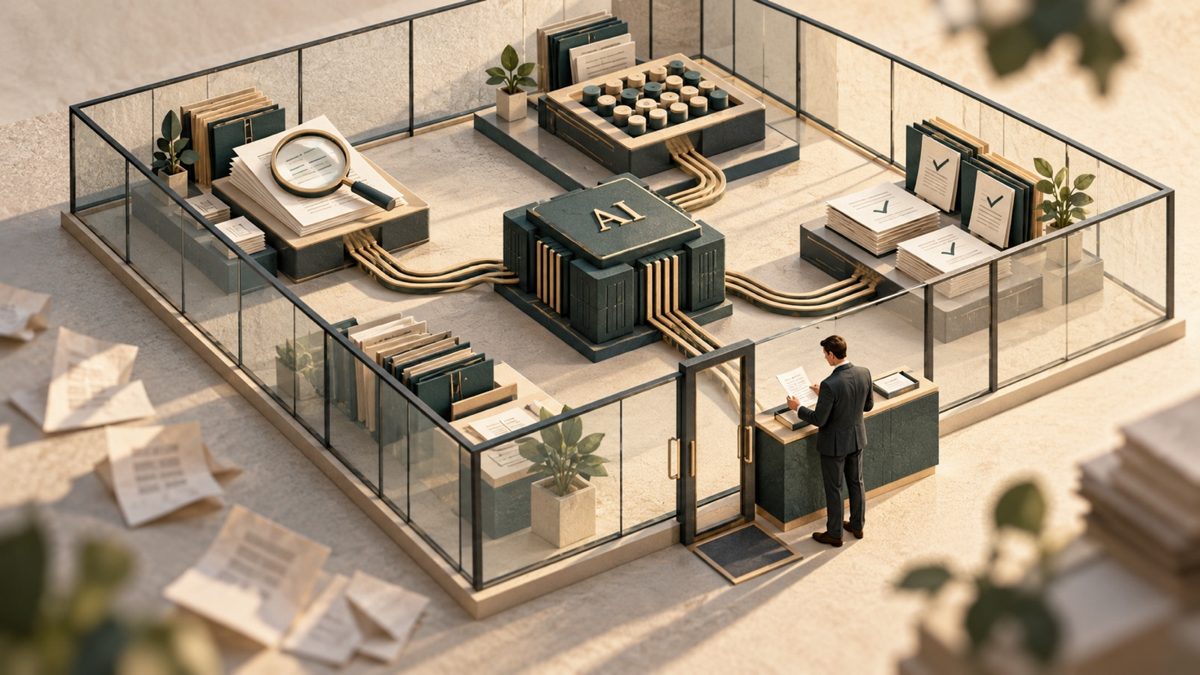
Consider a compliance application. The AI might identify passages relevant to a requirement and prepare a proposed assessment. Company-defined software can then check that the references exist, require completion of specified fields and prevent the proposal from becoming an approved finding without an authorised reviewer.
The distinction between interpretation and calculation is equally important. Where a result depends on an established formula, that formula should be implemented and tested in conventional software. A language model may help explain the result, but it should not silently invent or change the calculation.
Give each engine a specific job
A document classification assistant, a maintenance support tool and a compliance analysis system have different purposes. They should not automatically share the same information, permissions or ability to act.
For each function, the company should define: the task the system is authorised to perform; the information it may access; the evidence required to support its output; the actions that require human approval; and the circumstances in which it must stop or report uncertainty.
This approach is consistent with the UK National Cyber Security Centre's guidance on secure AI design, which recommends assessing deployment choices, restricting possible actions and applying least-privilege principles. Its guidance explicitly covers existing models and external services as well as systems developed in-house.
Boundaries must exist outside the prompt
Instructions such as "keep this confidential" or "use only these documents" are useful, but they are not sufficient security controls.
Permissions, network restrictions and approval requirements must also be enforced by the surrounding software and infrastructure. A model should not gain access to an entire customer archive simply because a document asks it to retrieve more information.
The NCSC identifies AI-specific threats, including prompt injection and data poisoning, alongside conventional cybersecurity risks. Security therefore needs to cover design, development, deployment and ongoing operation.
Security must be demonstrated
"Proprietary," "private" and "specialised" describe aspects of a system. None proves that it is secure or accurate.
A company-controlled engine still needs representative testing, access reviews, protected logs, controlled updates and a workable incident response process. Human review also needs substance: reviewers must have the expertise, evidence and time to challenge an output.
The strongest business case for dedicated AI is the ability to define and verify these conditions. A company should be able to explain what its system does, what information it uses, where its authority ends and who remains responsible.
That is the foundation for dependable enterprise AI: a clearly defined function, governed by explicit rules, operating within enforceable boundaries.
Sources
- NIST, Generative AI Risk Management Profile
- EDPB, Opinion on AI Models
- NCSC, Secure AI Design
- NCSC, Guidelines for Secure AI System Development
This article is informative and does not replace professional advice on a specific case.